Your software product has passed the technical evaluation, pricing discussions are complete, and an enterprise customer is ready to proceed. That’s when procurement requests your latest SOC 2 report. You don’t have one.
This situation creates an immediate challenge for Australian SaaS companies entering larger markets. Because security assurance takes time, rushing into the wrong assessment may not satisfy the customer’s requirements. Understanding what the buyer expects, and planning backward from the deadline, is where the solution begins.
A calm first step is to find out exactly what was asked for, and by when. The request can leave more room than it first appears to, so ask before you assume.
Which SOC 2 Report Does the Customer Need?
Different SOC 2 reports provide different levels of assurance. Enterprise security requirements make the distinction between SOC 2 type 1 vs type 2 matter. Type 1 looks at whether relevant controls are suitably designed as of a particular date. Over a defined period, Type 2 examines both their design and their operating effectiveness.
An enterprise buyer may accept Type 1 temporarily, but many specifically request Type 2 because it provides evidence covering actual operations. Prior to commissioning an examination, confirm with the customer the report type, the required scope, and acceptable reporting dates.
Write the answers down, since the report type, scope, and dates all drive the plan and the budget.
Plan Your Timeline Around the Observation Period
A SOC 2 type 2 examination cannot be completed simply by preparing documentation and scheduling an auditor. Throughout the reporting period, the organization must operate its relevant controls. An initial examination may cover a period of three months, whereas subsequent reports commonly cover longer ones.
Where your business needs to demonstrate access reviews, security training, or change approvals, those activities must happen, and be documented, during the applicable window. Planning backward from a customer deadline helps identify whether the requested report can realistically be delivered on time.
If the deadline is tighter than the observation period allows, tell the customer early. Some customers are willing to discuss interim steps, such as a dated plan, when they hear about the gap early.
Understand What You Are Actually Buying
Although SOC 2 does not issue certificates, businesses frequently search for SOC 2 type 2 certification.
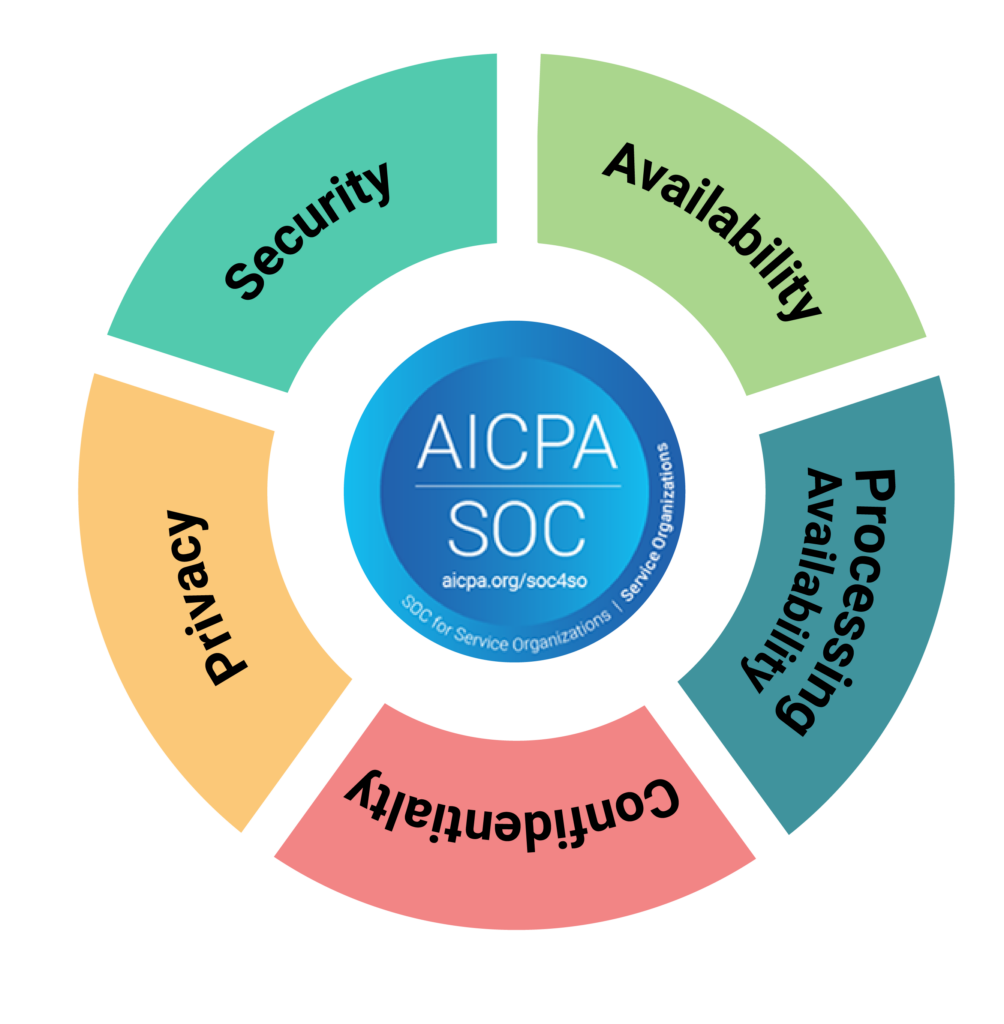
A licensed CPA firm issues an attestation report after performing an independent examination against the applicable AICPA Trust Services Criteria. The report describes the assessed system, relevant controls, testing procedures, and the auditor’s opinion.
Often under a confidentiality agreement, that document is what customers typically review. A SOC type 2 report also relates to a specific historical period. It does not automatically provide assurance about every change made afterward.
Understand the Costs Before You Begin
An independent examination fee is only part of the cost of SOC 2 preparation. Assistance with developing policies, conducting risk assessments, preparing evidence, training employees, and arranging security testing may be needed.
For businesses with up to 50 employees, Siege Cyber advertises a SOC 2 compliance package at AUD $2,750 per month, excluding GST, over twelve months. The advertised offer applies to eligible contracts that are signed by December 31, 2026. The package includes compliance preparation, training, a compliance platform, and external penetration testing.
The independent CPA examination is billed separately, with Siege Cyber indicating typical fees of approximately AUD 5,000–15,000, depending on scope and complexity. Make sure you confirm current pricing, eligibility, and deliverables before committing.
What If Your Report Is Already Outdated?
Suppose your Type 2 report covers January through June, but a customer requests assurance in October. The intervening months fall outside what the report examines. Relevant changes since the reporting period ended can be described in a management-issued bridge letter, which some customers may accept.
A bridge letter does not replace an independent examination, and acceptance depends on the customer’s requirements. Don’t assume an older report will satisfy procurement; discuss reporting gaps early.
Get More From Your Compliance Investment Than One Contract
Siege Cyber provides Australian-based SOC 2 readiness support with fixed-price consulting packages and independent audit coordination. Growing software companies get the most from connecting compliance preparation with actual operational responsibilities.
Assign control owners, maintain security records, and establish a reporting schedule that supports future customer reviews. A successful SOC 2 project should leave your business better prepared for the next enterprise opportunity, not simply help it respond to the current request.
Keep the evidence you collect organized from the beginning, and the next audit cycle becomes less of a scramble. Controls are more likely to keep operating between audits when responsibilities and schedules are reviewed at regular intervals.